KRI Library (152 Key Risk Indicators)
152 KRIs — including 20 emerging-risk KRIs for AI-enabled fraud, scams and AI governance — with thresholds, owners and a calculating dashboard.
Price
$49
One-time. No subscription. Use forever.
Delivered immediately after checkout — your template and guide links are emailed to you with your receipt.
Built for risk and compliance teams at financial-services organizations
◆ Quick buying summary
What you get and when you can use it
- Good fit if
- You have a risk register but no way to monitor whether risk levels are actually changing
- Format
- Editable workbook plus PDF/supporting guide materials where included. Instant download after checkout.
- Need the methodology first?
- Read the KRI Library Template Guide.
- Time to value
- Start reviewing, editing, and assigning owners the same day; customize to your organization before sharing outputs externally.
- After purchase
- After payment, download every file immediately from the confirmation page. RiskTemplates also emails a secure access link, and Stripe sends the payment receipt separately. No account required.
◆ What's included
- ◆ 152 pre-built KRIs across 23 risk categories, each with 24 fields of metadata
- ◆ 20 emerging-risk KRIs (AI-enabled fraud, scams, instant payments, AI governance, AI agents), each with its source
- ◆ Board / Management / Operational tier on every KRI, plus Emerging Risk filter
- ◆ KRI Dashboard that calculates Green/Amber/Red status, trend and breach streaks from your values
- ◆ 11 BSA/AML KRIs, including SAR timeliness, OFAC coverage, CDD/EDD and alert aging
- ◆ Implementation roadmap covering every KRI, plus board, management and exception report templates
- ◆ 26-page guide: KRI selection, threshold calibration, escalation protocol, reporting cadence
Use rights: customize for internal business use and use outputs with your auditors, customers, bank partners, and regulators. Do not resell or redistribute the template files.
◆ Preview
See what the template covers.

152 KRIs across 23 risk categories — the library at a glance
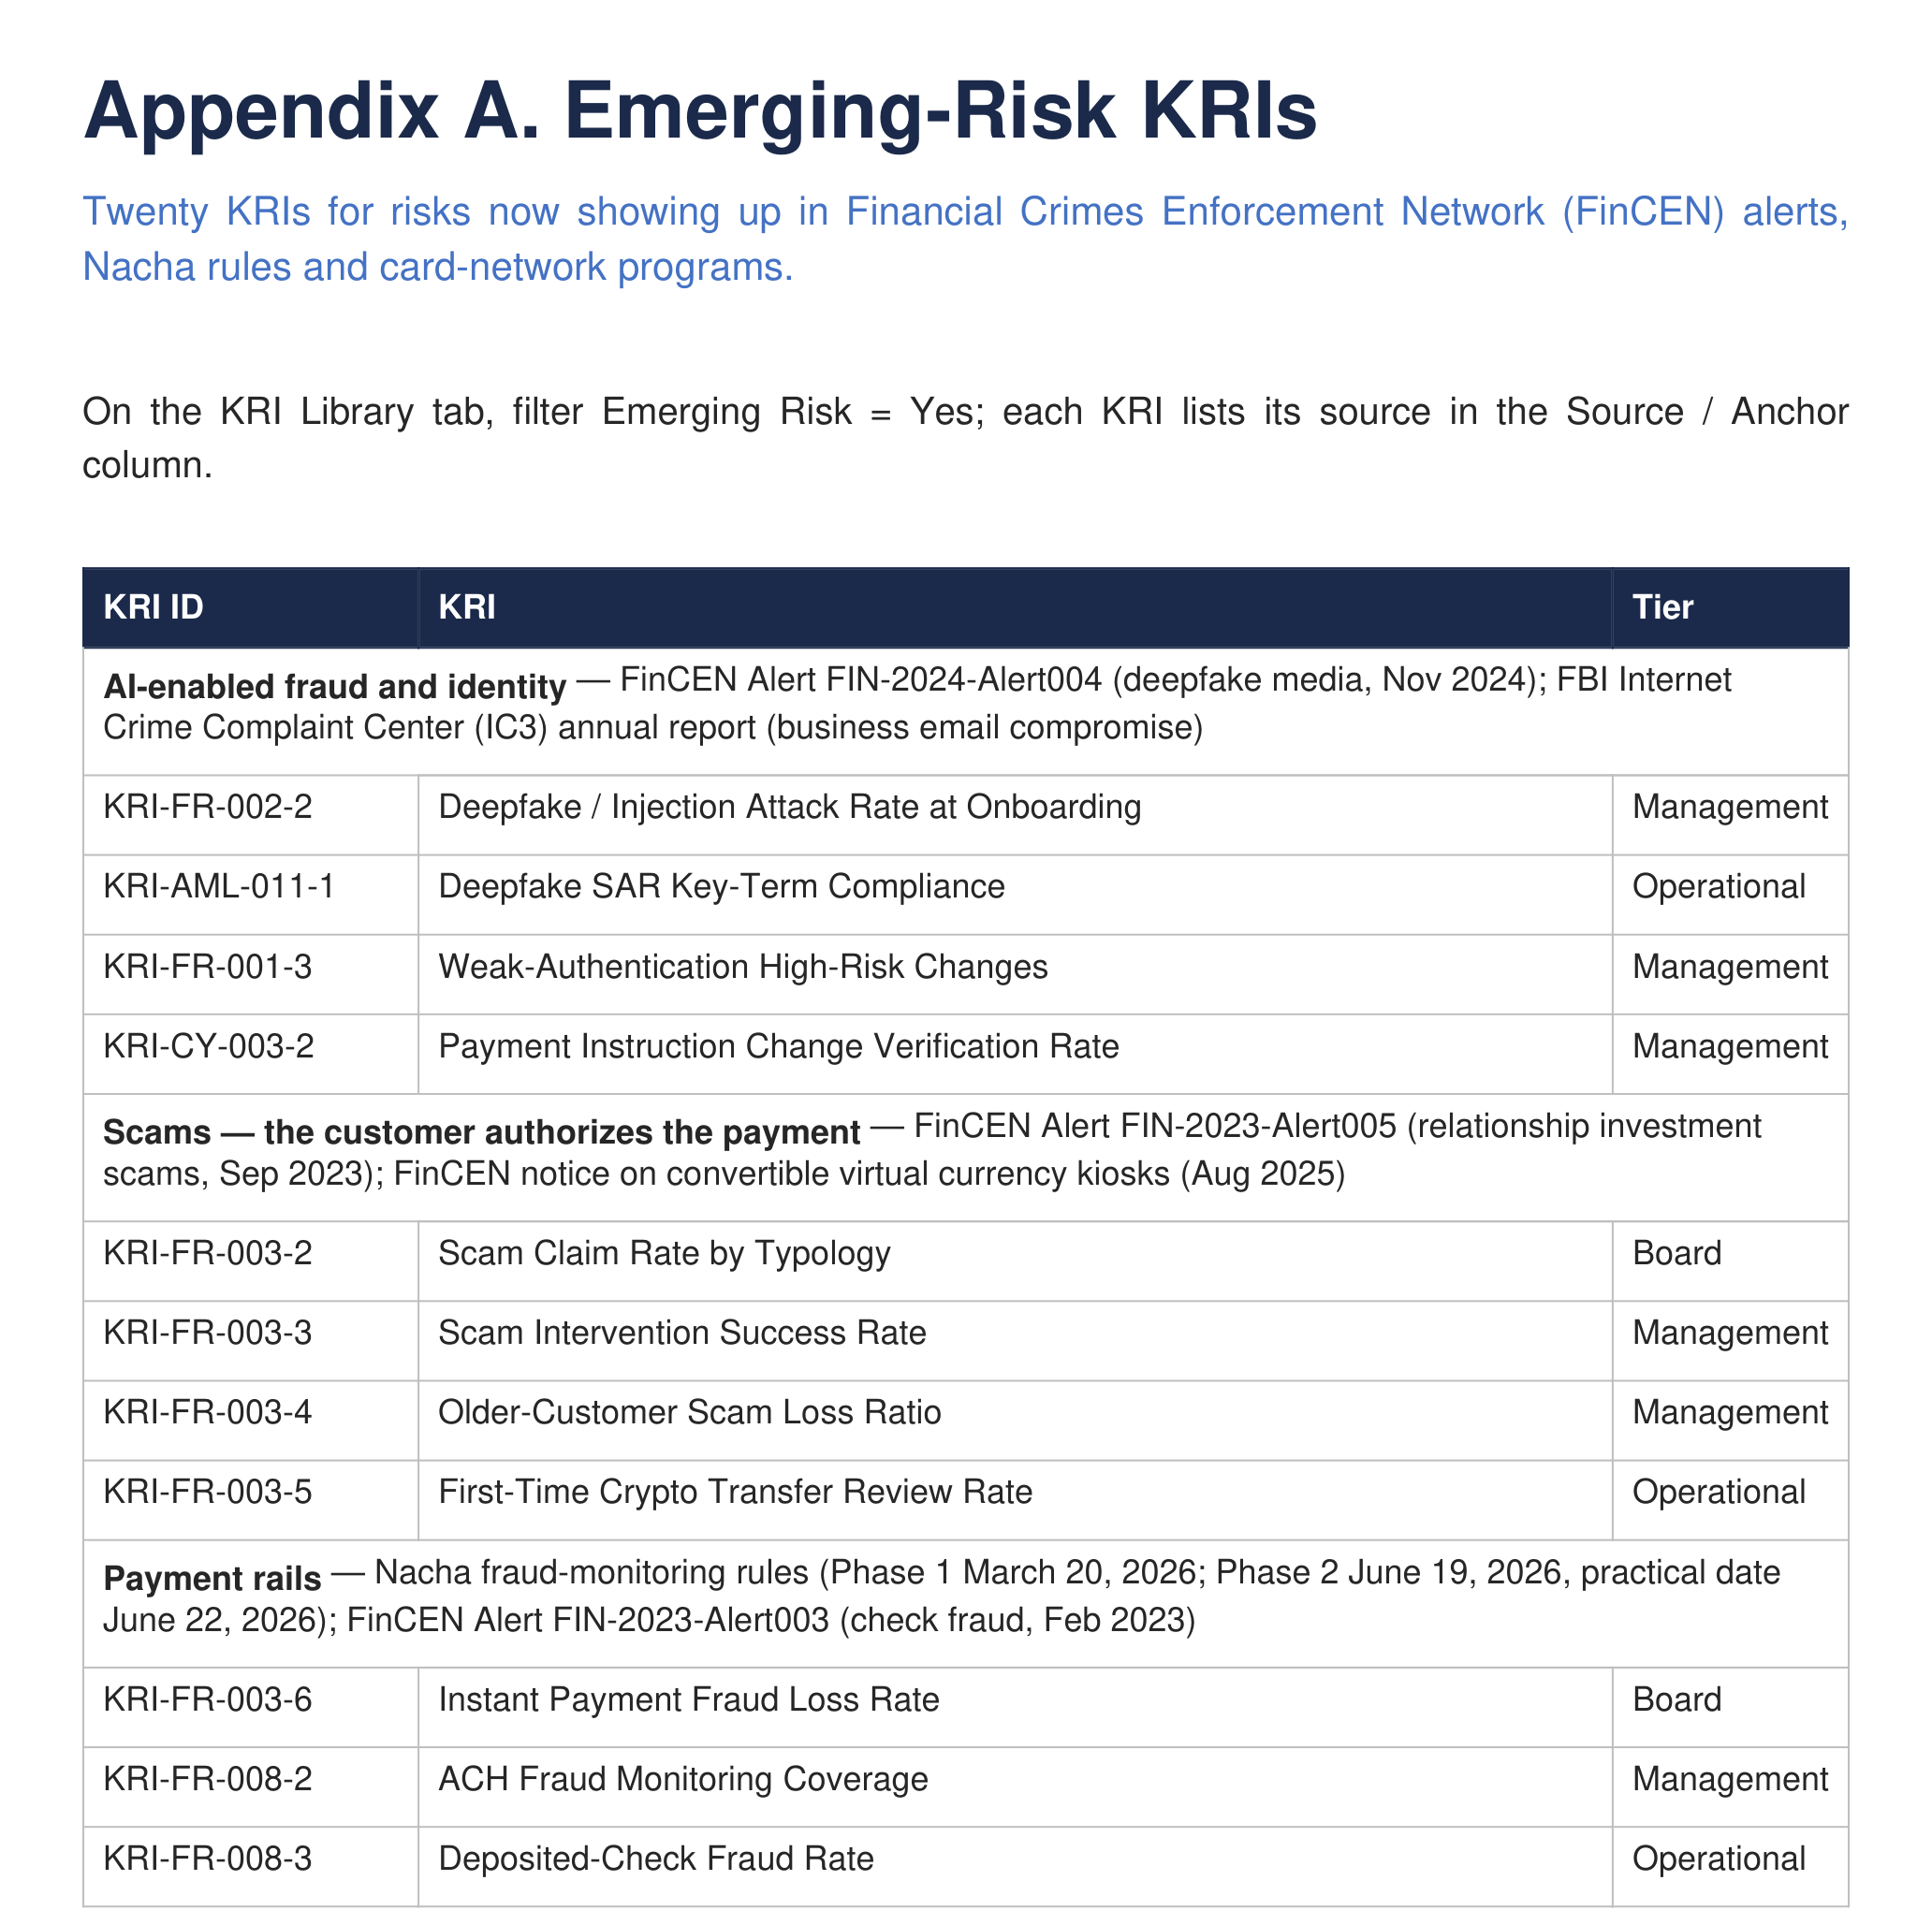
20 emerging-risk KRIs — AI-enabled fraud, scams, payment rails, AI governance and AI agents, each with its source

The 24 fields on every KRI — definition, thresholds and rationale, data source, owner, escalation trigger, tier and source
◆ Template guide
KRI Library Template Guide
How to build a Key Risk Indicator (KRI) library: metric definitions, calculation formulas, green/amber/red thresholds, data sources, owners, and escalation triggers — with real examples.
◆ FAQ
Frequently asked questions.
What does the library cover?
152 KRIs across 23 categories. The largest are Fraud (19), Vendor/Third-Party (12), Technology, Cyber and BSA/AML (11 each), Operational (10) and AI & Automation (9), followed by Strategic, People, Model, Bank Partner, Reputational, Financial, Lending, Payments, Compliance, Legal, Crypto, Embedded Finance, Stablecoin, BaaS, Insurtech and Wealthtech risk. Filter by category, tier or emerging risk to build your own set.
What are the emerging-risk KRIs?
Twenty KRIs added in September 2026 for risks now appearing in FinCEN alerts, Nacha rules and card-network programs: deepfake and injection attacks at onboarding, weak authentication on high-risk account changes, payment-instruction fraud, scam claim rates and intervention success, older-customer scam exposure, first-time crypto transfers, instant-payment and deposited-check fraud, Nacha fraud-monitoring coverage, AI assessment currency, shadow AI, sensitive data in AI prompts, chatbot accuracy, human override rates, vendor AI model changes, AI provider concentration, and AI agents that initiate payments. Each lists the alert, rule or program it is anchored to.
How do the tiers work?
Every KRI is tagged Board (19), Management (117) or Operational (16). The Board tag marks candidates: pick the 5–8 that match your top risks for the board pack, 10–15 Management KRIs for the executive or risk committee, and Operational KRIs as needed. Filter the library by tier to build each pack.
Does the dashboard calculate status automatically?
Yes. Enter this period's value (and last period's) and the dashboard calculates Green/Amber/Red status, prior status, trend, and how many periods each KRI has been out of Green, with summary counts by tier and category and a list of Red KRIs. Thresholds come from each KRI's threshold logic, which you can edit when you recalibrate.
Are the thresholds industry benchmarks?
They are starting points. Established KRIs carry thresholds based on common practice, with the reasoning written out so you can adjust them; benchmark figures are labeled as commonly cited ranges to validate against your own data. The emerging-risk KRIs use starter thresholds because no reliable benchmark exists yet — the guide explains how to recalibrate after three months of your own data.
Can I use this KRI library without a formal risk register?
Yes. The library works standalone. Each KRI also carries a linked risk ID that matches the free Risk Register, so if you use both, your KRIs map straight to your risks.
Can I share completed outputs externally?
Yes. You can use completed outputs with auditors, customers, bank partners, regulators, and internal stakeholders. Customize the template for internal business use — just don't resell or redistribute the source template files.
How do I receive the files?
Checkout is handled through Stripe. After payment, download every file immediately from the confirmation page. RiskTemplates also emails a secure access link, and Stripe sends the payment receipt separately. No account is required.
What if it's not a fit?
Email within 30 days for a full refund, no questions asked. The guarantee is meant to remove purchase risk while you evaluate whether the template fits your use case.
● First-time buyer offer
Get 20% off your first template.
Drop your email and we'll send the code.
◆ Not ready to buy?
Start with the free Risk Register.
141 pre-populated fintech risks across 21 categories. ISO 31000 structure.
Download free Risk Register →◆ Related templates
Pairs well with.
Risk Register — Fintech Edition (Free)
141 pre-populated fintech risks across 21 categories. ISO 31000 structure. Ready to use in a week.
RCSA (Risk & Control Self-Assessment)
141 fintech risks with mapped controls, a 97-question self-assessment, control testing plan, challenge log and a one-page Board Summary.
Enterprise Risk Management Framework (ERMF)
Complete ERM documentation: risk appetite, 3 Lines of Defense, committee charter, and board reporting.
◆ Ready when you are
Get the KRI Library (152 Key Risk Indicators).
Start building a defensible risk program today.