Data Privacy Compliance Kit for Fintechs
Which of the 23 state privacy laws apply to your fintech after GLBA, plus the GLBA checklist, request tracker, assessments and vendor terms to comply.
Price
$69
One-time. No subscription. Use forever.
Delivered immediately after checkout — your template and guide links are emailed to you with your receipt.
Built for risk and compliance teams at financial-services organizations
◆ Quick buying summary
What you get and when you can use it
- Good fit if
- You assumed GLBA exempts you from state privacy laws and need to check state by state
- Format
- Editable Excel workbook (12 tabs) plus a 17-page PDF implementation guide. Instant download after checkout.
- Need the methodology first?
- Read the Data Privacy Compliance Template Guide.
- Time to value
- Start reviewing, editing, and assigning owners the same day; customize to your organization before sharing outputs externally.
- After purchase
- After payment, download every file immediately from the confirmation page. RiskTemplates also emails a secure access link, and Stripe sends the payment receipt separately. No account required.
◆ What's included
- ◆ GLBA-aware applicability for all 23 state privacy laws: Applies, Applies to non-GLBA data, Exempt or Not triggered
- ◆ State Law Reference: thresholds, GLBA exemption type, deadlines, opt-out signals, sensitive data, assessments, cure periods, penalties and sources
- ◆ GLBA checklist: Regulation P notices and opt-outs, and all ten Safeguards Rule elements with small-institution relief
- ◆ Data inventory that tags GLBA nonpublic personal information (NPI) and state-law sensitive data
- ◆ Retention schedule built on federal record-keeping rules
- ◆ Data protection assessment register and filled-in template
- ◆ Consumer request tracker with deadlines by state and request type
- ◆ Vendor contract terms review and a 2026–2028 regulatory watchlist
Use rights: customize for internal business use and use outputs with your auditors, customers, bank partners, and regulators. Do not resell or redistribute the template files.
◆ Preview
See what the template covers.
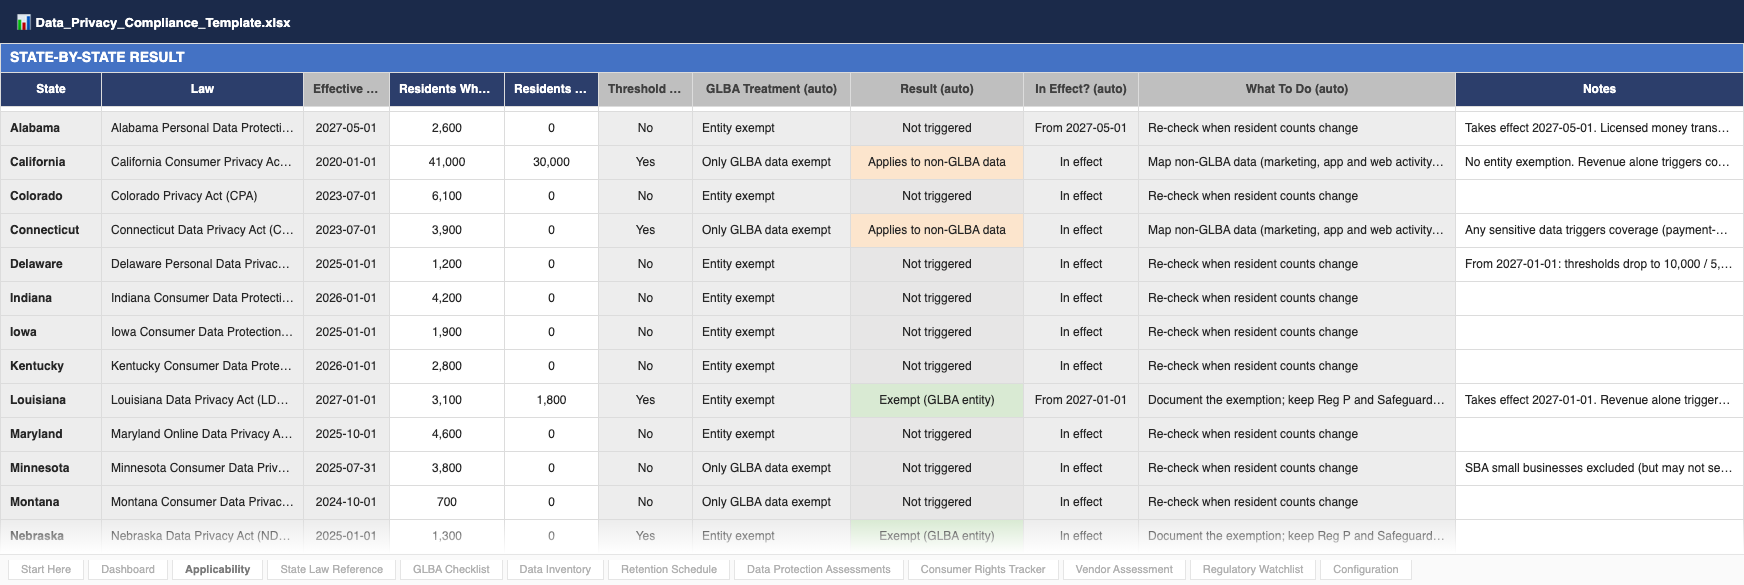
Applicability — GLBA treatment and result for each state privacy law, from your profile and resident counts
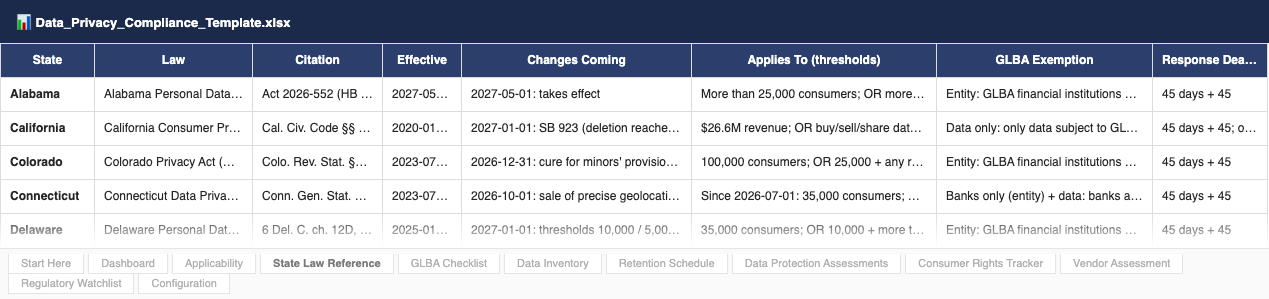
State Law Reference — thresholds, GLBA exemption type and deadlines for 23 state privacy laws
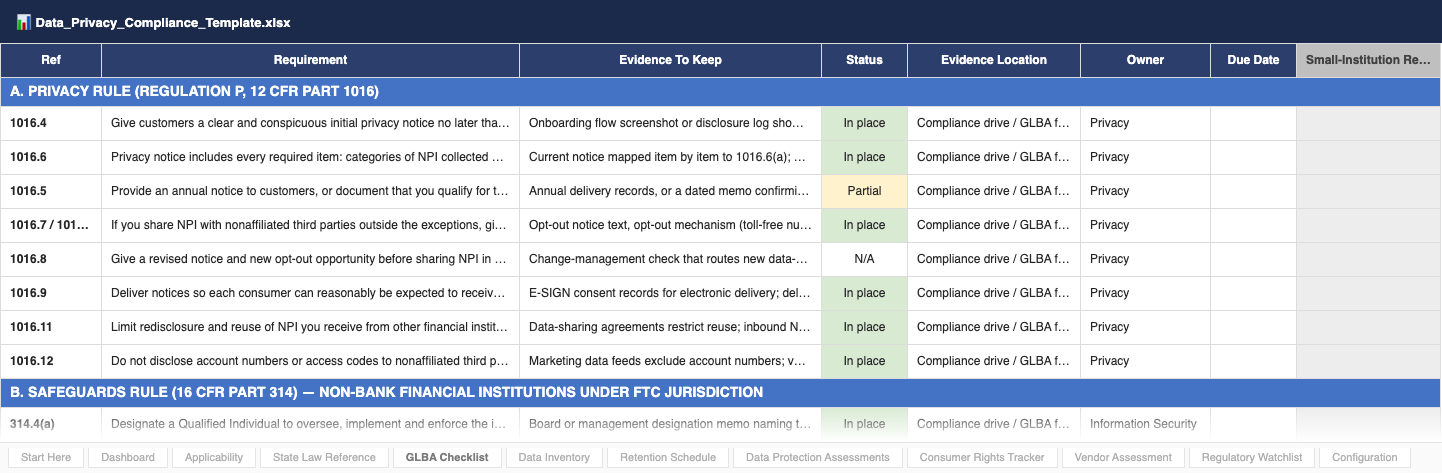
GLBA Checklist — Regulation P and Safeguards Rule requirements with evidence to keep
◆ Good fit if any of these sound familiar
When teams reach for this template.
You told your bank partner state privacy laws don't apply because you're GLBA-covered.
That is still true in many states, but not in California, and not for non-bank fintechs in Connecticut (since July 2026), Montana (since October 2025), Oregon or Minnesota — with Delaware (2027) and Vermont (2028) to follow. The Applicability tab shows exactly where you stand.
Privacy requests arrive by email and nobody tracks the deadline.
The tracker computes each deadline from the consumer's state and request type and shows what is overdue or due this week.
Your Safeguards Rule program exists, but you couldn't show the evidence for each element.
The GLBA Checklist lists every requirement with the evidence to keep, an owner and a status.
◆ Why now
The GLBA exemption is narrowing and four new state laws start in 2027–2028
Connecticut moved non-bank fintechs to a data-only exemption on July 1, 2026; Delaware follows in January 2027. Oklahoma, Louisiana, Alabama and Vermont enacted laws in 2026, and California's automated decision-making and risk-assessment rules phase in from 2027. The kit is current to September 2026 and lists its sources so you can re-check.
◆ Where this fits
Where this fits in your risk program
- ◆ Start here if you need to know which privacy laws apply and what they require.
- ◆ Pair it with the Incident Response kit for breach notification.
- ◆ Pair it with the TPRM kit to add processor terms to your vendor inventory.
- ◆ Use the AI Risk Assessment Template alongside it for automated decision-making.
◆ What this isn't
Setting expectations.
- × Not legal advice — a working tool to organize your program and your questions for counsel.
- × Not software — an Excel workbook and a PDF guide.
- × Not GDPR or international coverage — US federal and state law only.
- × Not a breach notification playbook — that's the Incident Response kit.
◆ 30-day rollout plan
A sample 30-day rollout
A starting sequence; adjust for your entities, data and resources.
- Week 1
Scope
Confirm GLBA status for each legal entity, count residents by state and complete the Applicability tab.
- Week 2
Data
Build the data inventory with GLBA and sensitive-data flags and set the retention schedule.
- Week 3
GLBA and vendors
Complete the GLBA checklist with evidence and fix missing processor terms.
- Week 4
Rights and assessments
Stand up request intake and tracking, update notices, and complete assessments for targeted advertising, sensitive data and automated decisions.
◆ Full playbook in the PDF guide
The 17-page guide explains each step, including how to answer requests where GLBA exempts part of the data.
◆ Regulatory alignment
Built on primary sources
Checked against the statutes and regulations in September 2026:
- ◆ 23 state comprehensive privacy laws (sources listed for each in the workbook; open items flagged)
- ◆ GLBA Privacy Rule — Regulation P (12 CFR Part 1016)
- ◆ GLBA Safeguards Rule (16 CFR Part 314), including the FTC notification requirement
- ◆ California CCPA regulations (11 CCR 7000 et seq.)
- ◆ Federal record-keeping rules: 31 CFR 1010.430, Regulations B, E and Z
Privacy laws change every legislative session. The State Law Reference and Regulatory Watchlist show what to re-check.
Last updated: September 29, 2026
◆ Template guide
Data Privacy Compliance Template Guide
How to build a fintech data privacy compliance template: GLBA status and state-law applicability, a data inventory that separates GLBA data, consumer request tracking with the right deadlines, and processor contract terms.
◆ FAQ
Frequently asked questions.
We're a GLBA financial institution. Do state privacy laws apply to us at all?
It depends on the state. Today 17 of the 23 laws exempt GLBA financial institutions entirely (Delaware narrows its exemption in January 2027). Five exempt banks and similar institutions entirely but give other fintechs only a data-level exemption (Connecticut since July 2026, Minnesota, Montana, Oregon and Vermont), and California exempts only GLBA data for everyone. Where only GLBA data is exempt, the law still covers your marketing, website and app activity, prospect and often employee data. The Applicability tab shows the result for each state.
How does the applicability check work?
You enter your GLBA status, revenue, whether you sell personal data or process sensitive data, and the number of residents of each state whose data you process. The workbook applies each state's tests — consumer counts, revenue from selling data, California's and Louisiana's revenue triggers, Connecticut's any-sensitive-data trigger, Texas and Nebraska's no-threshold rule — and the GLBA exemption type. It is a screening tool; confirm exemptions with counsel.
What GLBA content is included?
A checklist covering the GLBA Privacy Rule (Regulation P: initial and annual notices and the annual-notice exception, opt-outs, revised notices, delivery, limits on redisclosure and account-number sharing) and all ten Safeguards Rule elements in 16 CFR 314.4, including the FTC notification requirement for events affecting 500 or more consumers. Items that don't apply to institutions with fewer than 5,000 consumers are marked automatically.
How are consumer request deadlines calculated?
From the date received, the consumer's state and the request type: 45 days plus a 45-day extension in most states, 90 days in Iowa, and 15 business days for California opt-outs and requests to limit sensitive data. The tracker flags requests due within ten days and anything overdue.
Does it cover GDPR?
No. The kit is built for US fintechs and covers US federal and state law only.
What about breach notification?
The Safeguards Rule's FTC notice is in the GLBA checklist. State breach notification laws and regulator and bank-partner notices are covered in the Incident Response kit.
Can I share completed outputs externally?
Yes. You can use completed outputs with auditors, customers, bank partners, regulators, and internal stakeholders. Customize the template for internal business use — just don't resell or redistribute the source template files.
How do I receive the files?
Checkout is handled through Stripe. After payment, download every file immediately from the confirmation page. RiskTemplates also emails a secure access link, and Stripe sends the payment receipt separately. No account is required.
What if it's not a fit?
Email within 30 days for a full refund, no questions asked. The guarantee is meant to remove purchase risk while you evaluate whether the template fits your use case.
● First-time buyer offer
Get 20% off your first template.
Drop your email and we'll send the code.
◆ Not ready to buy?
Start with the free Risk Register.
141 pre-populated fintech risks across 21 categories. ISO 31000 structure.
Download free Risk Register →◆ Related templates
Pairs well with.
Incident Response & Breach Notification Kit
Run an incident and every notice clock it starts: bank partner, the bank regulators' 36-hour rule, NYDFS, FTC, SEC and breach laws in 54 states and territories. Workbook, guide, four playbooks, tabletop kit and Word plan templates.
Third-Party Risk Management (TPRM) Kit
Complete vendor risk management lifecycle from initial due diligence to ongoing oversight.
Business Continuity & Disaster Recovery (BCP/DR) Kit
BCP and DR templates with BIA, recovery procedures, and a standalone tabletop exercise kit.
◆ Ready when you are
Get the Data Privacy Compliance Kit.
Start building a defensible risk program today.